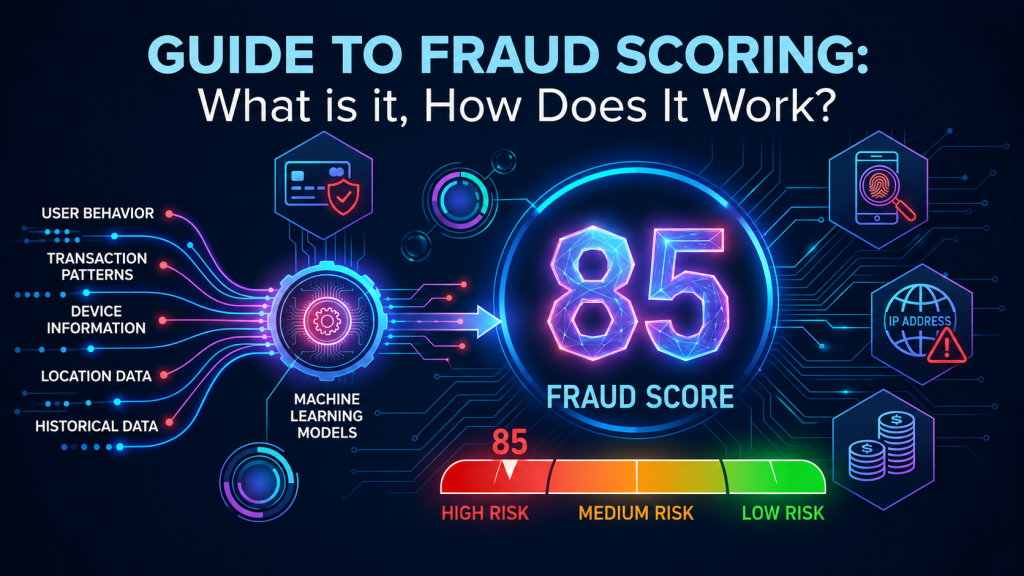
Dual-Sided Screening
Risk scoring for both payer and beneficiary, before or during transaction execution.
 Pilot Program for Financial Institutions → Try Now
IDYC360 is a privacy-first, entity-centric fraud intelligence platform that connects behavioural, geo-behavioural and network insights to identify suspicious patterns, assess risk in real time and uncover potential mule networks—within and across financial institutions, without sharing raw customer data.
Assess payment risk, monitor changing entity behaviour and investigate connected networks through one fraud-intelligence platform.
Real-time payer/beneficiary risk scoring, mule-network graph analysis and geo-behaviour intelligence, combined into a single decision.
Explore Fraud Detection →
Behaviour history, velocity and pattern-deviation signals streamed continuously to feed every risk decision.
Explore Transaction Monitoring →
Instant payment screening evaluates every transaction using real-time risk checks preventing fraud proactively.
Explore Payment Fraud Risk Assessment →Institutions monitor transactions institution-by-institution, while fraud rings operate across accounts, geographies and entities—limiting how much of the wider network one institution can observe.
Single-bank visibility misses the network
IDYC360 checks the risk of the payer, beneficiary, relationship, geography and network before or during a transaction, then returns an explainable risk decision.
Who is initiating the transaction?
Who receives the money?
Is this relationship normal?
Is this location pattern risky?
Is this part of a suspicious ring?
The bank sends a transaction event; IDYC360 enriches it with risk context and returns an action-ready decision.
Amount, payer, beneficiary, channel and metadata.
Behaviour history, geo baseline and network signals.
Risk band, reason codes and recommended action.
Alerts, dashboard, evidence trail and audit.
Runs as an API layer, private cloud, on-premise, or controlled pilot environment—enhancing existing fraud and AML systems without replacing them.
From instant payment fraud to complex mule networks—connected intelligence supports payment-risk assessment and network investigation.
Assess payment activity using entity behaviour and connected context. Supported channels and response-time criteria are agreed for each deployment.
Explore potential mule networks and connected paths within the data available to the institution.
Continuous behavioural analysis across channels with STR-ready cases and complete audit trails.
Organise risk explanations and entity/network context to support the institution’s investigation and reporting workflow.
Examine geographic shifts and concentrations alongside entity behaviour and relationship signals.
Identify unusual changes in entity activity that warrant investigation.
Designed for the compliance, integration and scale requirements of Indian financial institutions.
Modernize fraud prevention without disrupting core banking systems.
Manage high transaction volumes with lean compliance teams.
Get enterprise-grade fraud intelligence at startup speed.
Gain cross-institutional intelligence and real-time risk visibility.
Six capabilities that separate IDYC360 from legacy rule-based systems and single-purpose AI tools.
Risk scoring for both payer and beneficiary, before or during transaction execution.
Graph analysis to detect rings, funnels, rotations and linked account clusters.
Pseudonymized entity intelligence without exposing raw customer PII in shared-risk models.
PIN-code, city and state hotspot intelligence for identifying emerging fraud clusters.
Risk band, reason codes and network context supporting audit-ready investigations, aligned with our Ethical AI & Model Governance Policy.
Architecture designed for high-volume BFSI transaction streams and enterprise deployment.
A comparison with legacy rule engines, enterprise AML suites and India-focused RegTech platforms. "Product-dependent" indicates capabilities that vary by vendor.
| Capability | Legacy Rules / SIEM | Global Enterprise Suites | India RegTech / KYC | IDYC360 |
|---|---|---|---|---|
| Dual-sided payer + beneficiary risk | Limited | Product-dependent | Limited | Core |
| Mule ring / network detection | Limited | Possible | Limited | Core |
| Cross-account / cross-FI model | Usually No | Product-dependent | Usually No | Designed for it |
| Privacy-preserving shared intelligence | Usually No | Product-dependent | Usually No | Core Design |
| PIN-code geo behaviour | Limited | Product-dependent | Limited | Available |
| India-specific deployment (RBI / FIU-IND) | Varies | Global-first, India via localisation | Strong | Built natively for India BFSI |
| Explainable evidence for investigation | Basic alerts | Varies | Varies | Risk reasons + graph context |
Final SLA and throughput are benchmarked in each bank's environment during a controlled proof of concept.
TPS lab range in synthetic tests
Decisioning target, optimised path
Controlled POC timeline
Scale-out production design target
Performance is validated during each bank proof of concept using agreed infrastructure, transaction volume and success criteria—so the institution can assess performance against its operating requirements.
Strengthen fraud detection, elevate AML effectiveness, and operate with confidence at scale.